Study: Credential Thieves Targeting Universities Using COVID Themes, Sophisticated Spoof Sites
- By Kristal Kuykendall
- 12/07/21
Cybersecurity experts at Proofpoint have identified a dramatic increase in phishing attacks targeting mostly North American universities, many of which leverage COVID-19 themes including testing information and the new Omicron variant.
In a Dec. 7 blog post, Proofpoint explained that credential-theft campaigns targeting universities and exploiting COVID-19 themes have ramped up consistently since October 2021. Following the announcement of the new Omicron variant in late November, the threat actors began leveraging the new variant in their attacks, Proofpoint researchers noted.
The threats targeting universities are interesting due to their specificity as well as their effort to mimic universities' legitimate login portals, the cybersecurity firm noted. "It is likely this activity will increase in the next two months as colleges and universities provide and require testing for students, faculty and other workers traveling to and from campus during and after the holiday season, and as the Omicron variant emerges more widely," the researchers said.
Proofpoint expects more threat actors will adopt COVID-19 themes given the introduction of the Omicron variant, based on previously published research that identified COVID-19 themes making a resurgence in e-mail campaigns following the emergence of the Delta variant in August 2021.
Campaign Details
Thousands of messages targeting dozens of U.S. universities have referenced the Omicron variant and COVID themes in recent weeks, according to Proofpoint.
The phishing e-mails contain attachments or URLs for pages intended to harvest credentials for university accounts. The landing pages typically imitate the university's official login portal, although some campaigns feature generic Office 365 login portals, the researchers noted.
In some cases, such as the Omicron variant lures, victims are redirected to a legitimate university communication after credentials are harvested. Proofpoint observed that these credential-theft attempts have already pivoted from Delta variant themes to Omicron themes since the announcement of the new variant just a few weeks ago.
E-mails with URLs use subjects lines such as "Attention Required - Information Regarding COVID-19 Omicron Variant - November 29," with a link to a spoofed landing page such as the example pictured below.
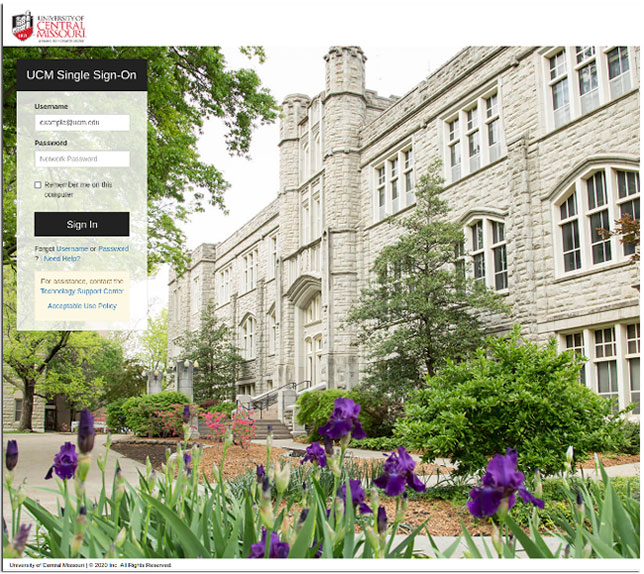
Spoofed login page for the University of Central Missouri
Messages distributing attachments included subject lines such as "Covid Test."
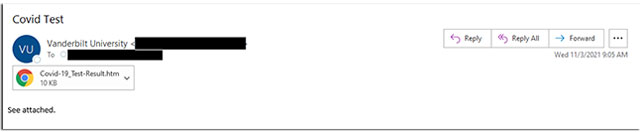
HTM attachment leading to a credential capture webpage
The attachments led to a university themed e-mail credential theft webpage.
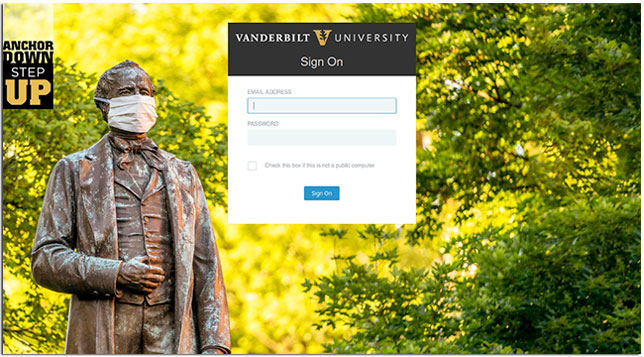
Credential theft webpage spoofing Vanderbilt University
In addition to multiple delivery methods of these ongoing threat attempts — Proofpoint has observed both URLs and attachments in campaigns — activity clusters use different sender and hosting methods to distribute credential-theft campaigns.
In the Omicron variant campaign, threat actors have leveraged actor-controlled infrastructure to host credential theft webpages using similar domain naming patterns. These include:
- sso[.]ucmo[.]edu[.]boring[.]cf/Covid19/authenticationedpoint.html
- sso2[.]astate[.]edu[.]boring[.]cf/login/authenticationedpoint.html
Attachment-based campaigns have leveraged legitimate but compromised WordPress websites to host credential capture webpages, including:
- hfbcbiblestudy[.]org/demo1/includes/jah/[university]/auth[.]php
- afr-tours[.]co[.]za/includes/css/js/edu/web/etc/login[.]php
- traveloaid[.]com/css/js/[university]/auth[.]php
In some campaigns, threat actors attempted to steal multi-factor authentication credentials, spoofing MFA providers such as Duo. Stealing MFA tokens enables the attacker to bypass the second layer of security designed to keep out threat actors who already know a victim's username and password.
To read more about ongoing cybersecurity threats, visit Proofpoint's blog.
About the Author
Kristal Kuykendall is editor, 1105 Media Education Group. She can
be reached at [email protected].