NIST Cybersecurity Framework Gets First Refresh
The National Institute of Standards and Technology (NIST) has released an update to its Cybersecurity Framework — the first since the guidance document was issued in 2014.
Cybersecurity Framework (CSF) 2.0's biggest change is the scope. While the government agency's original framework focused on securing critical infrastructure, 2.0 expands to include guidance for all organizations and enterprises — no matter their size or focus. NIST said the expansion was due to public sentiment on expanding the purpose of the Cybersecurity Framework to help provide personalized guidance for all against current threats.
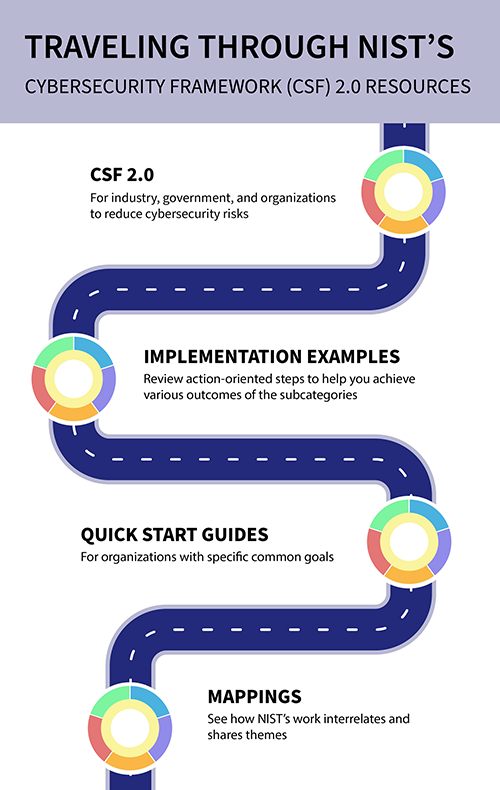 [Click on image for larger view.] Figure 1. Breakdown of what is new in the Cybersecurity Framework 2.0.
"The CSF has been a vital tool for many organizations, helping them anticipate and deal with cybersecurity threats," said Under Secretary of Commerce for Standards and Technology and NIST Director Laurie E. Locascio. "CSF 2.0, which builds on previous versions, is not just about one document. It is about a suite of resources that can be customized and used individually or in combination over time as an organization’s cybersecurity needs change and its capabilities evolve."
CSF 2.0 will provide quick-start guides for different types of organizations, implementation examples, and a suite of resources to assist in the adoption of the framework. New for 2.0 is the Reference Tool, designed to simplify the implementation process by allowing users to browse, search, and export information from the framework in both human and machine-readable formats.
Also arriving for 2.0 is a searchable catalog of informative references, enabling organizations to map their cybersecurity activities against the CSF and reference over 50 other cybersecurity documents. According to the government agency, the new resource expansion will be able to cater to both cybersecurity beginners and pros.
"As users customize the CSF, we hope they will share their examples and successes, because that will allow us to amplify their experiences and help others. That will help organizations, sectors and even entire nations better understand and manage their cybersecurity risk," said Kevin Stine, chief of NIST’s Applied Cybersecurity Division.