Stanford University
Project: Mobile Device Management Project lead: Kim Seidler, computer resource consulting director Technologies used: Developed in-house |
Stanford University's (CA) IT Services would have been very happy to purchase a commercial product that could address security issues relating to the BYOD (bring your own device) wave on campus. But there just wasn't one.
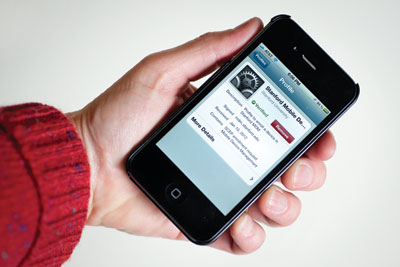
Stanford's Mobile Device Management solution balances user privacy with improved security compliance. (Photo by Linda A. Cicero / Stanford News Service) |
"This doesn't have anything to do with the vendors' shortcomings per se," explains Bruce Vincent, chief IT architect and technology strategist at the university. "What's missing is more related to the volatility of this whole sector. There are so many permutations of what's out there in the mobile space--and it's changing so rapidly--that the managed mobile device products just can't reasonably keep up." This is especially true in higher education, where locking down nonstandard devices and setting up firewalls are not typical of the culture.
So Stanford decided to develop its own solution for mobile device management (MDM) specifically for the higher education environment. The initiative fell to project lead Kim Seidler, computer resource consulting director in IT Services, and a large and diverse team of the university's most knowledgeable experts in security and mobile technologies, drawn from numerous departments and organizations. Key contributors include project manager Larry Ebert, strategists Vincent, Mark Mellis, and Scotty Logan, and development staff Adam Lewenberg, Chris Angelini, Sara Cook, and Yue Lu.
Once under way, the project team worked quickly: The MDM project was launched in March 2011, and the initial product went into production before the fall 2011 semester. In tackling the project, the team sought to build on the university's existing virtual infrastructure. As the predominant mobile platform on campus, Apple iOS was selected as the initial client platform. Open source technologies were selected for existing developer skill sets and known best practices.
Another important goal was to create transparency for the user, since registration of devices is voluntary. Besides the technical benefits that come from having a registered device, a sense of goodwill is helpful in influencing user behavior and increasing adoption. "The transparency is mostly about making the device owner aware of everything we know," says Vincent. "One driving premise of Stanford's MDM effort--which also shaped why we built this service instead of buying--was that we actually don't want to have access to any user data through this service. We want to access the very minimum we need to secure devices."
Among the carrots that encourage participation are:
- Automated or simplified device configuration: e-mail, calendaring, contacts, and VPN access
- Remote, self-service functionality: resetting the device or passcode remotely, or electing to erase Stanford-only data or all data remotely if the device is lost or stolen
- Enhanced privacy and protection: secure access to nonpublic data from iPhones, iPads, or iPod Touch devices
- No cost: MDM is provided free to Stanford staff, students, and faculty.
A very simple registration page asks users to indicate if they are dealing with sensitive data. If so, the system sets up additional security functions such as stronger passcodes or encryptions, and shortened timeout periods.
"MDM is elective at this point," notes Vincent. "But the direction it's going is that individuals who have certain roles in the university will need to make sure they are compliant. Right now, it's a local, departmental issue, but that may change. The risk isn't increasing because the devices are getting less secure--actually they are getting more secure. But the fact is that more university business is being conducted on these devices. We have to pay attention to that."
The MDM service is designed to be adaptable as university policies evolve. With the cultural shift toward mobile computing and the challenges of creating a secure BYOD environment, MDM is an important and growing part of the university's overall security strategy.
About the Author
Meg Lloyd is a Northern California-based freelance writer.